- bola
- access-control
- methodology
- beginner
How I Found My First HackerOne Bounty: a Missing Auth Check Hiding in Plain Sight
· matty69v
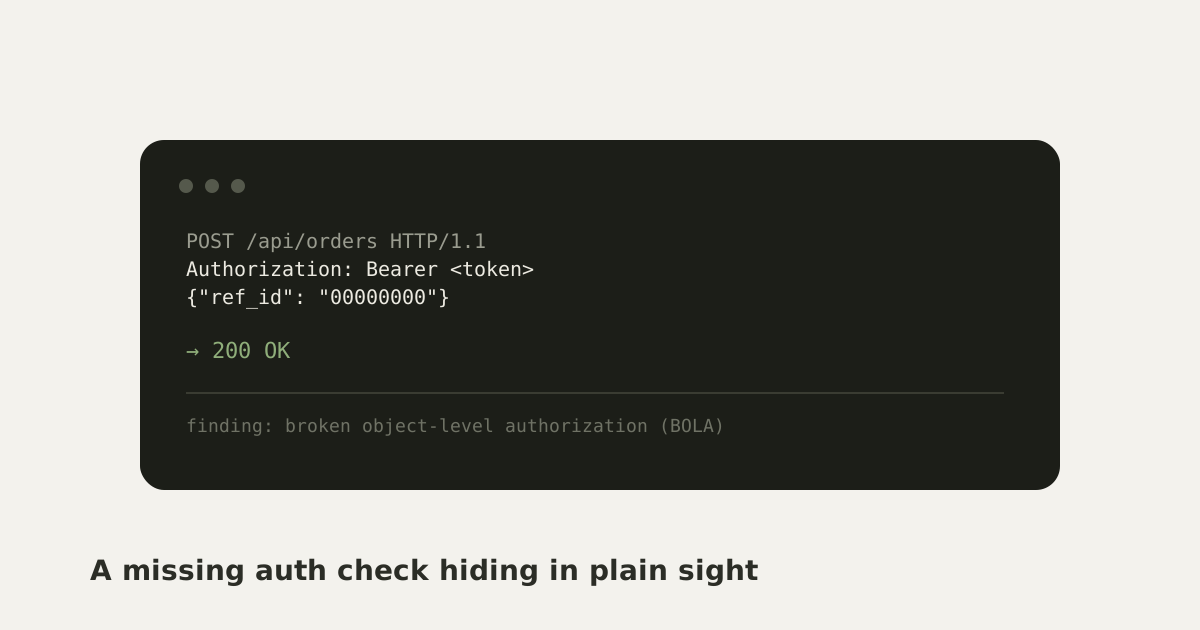
First valid finding after months of trying, on a mid size company (8 figure revenue, real production API). The bug was almost embarrassingly simple, so here is the thought process, because a lot of beginners overlook this exact class.
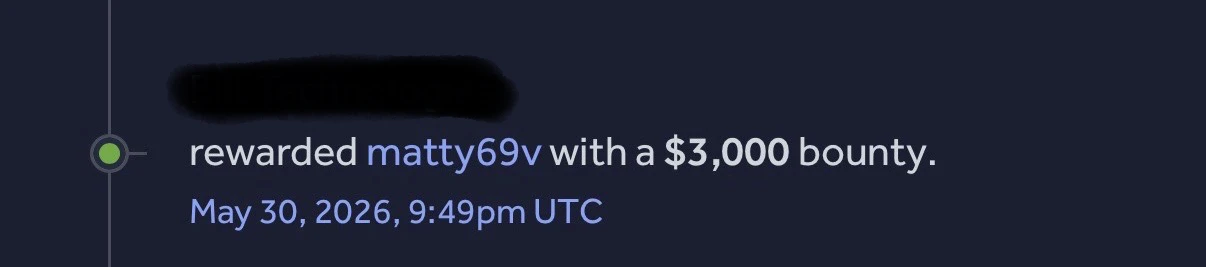
I did part of the recon and the report writing with a set of AI agents I run from my terminal. Proof of the approved report (target redacted) is below.
Stop chasing RCE. Ask "who is allowed to do what?"
Everyone starting out hunts injection and RCE. Those are hard and heavily tested. What actually pays beginners is broken access control, because it needs no exotic payload, just questioning an assumption the developers made.
The core question on every endpoint: what does the server actually verify, versus what does it just trust the client to send?
The finding
I picked a company that ships fast (public API, rewards product, lots of user generated content) and spent day one just understanding how a normal user creates data.
Then I found an endpoint that created content and ran the dumbest possible test: I removed the authentication header and resent the request.
200 OK. No token, no account, no prior transaction required.
Two things made it worse. The ID meant to prove you had a real prior interaction? The server accepted anything, including all zeros, and never checked it. And the resource IDs were sequential integers, so the response leaked roughly how many real records existed in production.
Textbook BOLA. Anyone could flood the platform with fake content anonymously, which breaks the trust the whole product relies on.
Lessons for your first hunt
- Test the absence of auth before clever bypasses. Just delete the token and resend.
- When an endpoint takes an ID meant to prove ownership, try garbage values. If the server does not reject them, you found something.
- Sequential integer IDs leak scale and let you enumerate.
- The report matters as much as the bug. Clear summary, minimal steps, honest impact, concrete remediation. That is the gap between "resolved + bounty" and "closed as informative."
Happy to answer methodology questions in the comments.
Comments
Loading comments…